 OWASP ASI01
Indirect Prompt Injection
Rogue data exfiltration via unmonitored PDF and email agent inputs — adversaries hijack agent context to leak credentials and proprietary data.
A 30-day institutional diagnostic for CISOs and executive boards. Identify unmonitored agentic security risks, eliminate redundant tool spend, and enforce NIST/OWASP governance.
20% advisory credit locked for 24h on your current IP / device.
A 4-minute executive briefing by Sagar Kulkarni — what an AI audit reveals beneath the surface of your enterprise stack.
Four vectors where unmonitored AI quietly erodes security posture, operational integrity, and capital efficiency.
OWASP ASI01Rogue data exfiltration via unmonitored PDF and email agent inputs — adversaries hijack agent context to leak credentials and proprietary data.
 ASI02
Unscoped API tokens and autonomous agent credential sharing leave persistent, unmonitored backdoors across your SaaS and cloud estate.
 ASI06
Supply chain, SCADA, and ERP logic manipulation in manufacturing — adversarial agents corrupt production logic and quality controls.
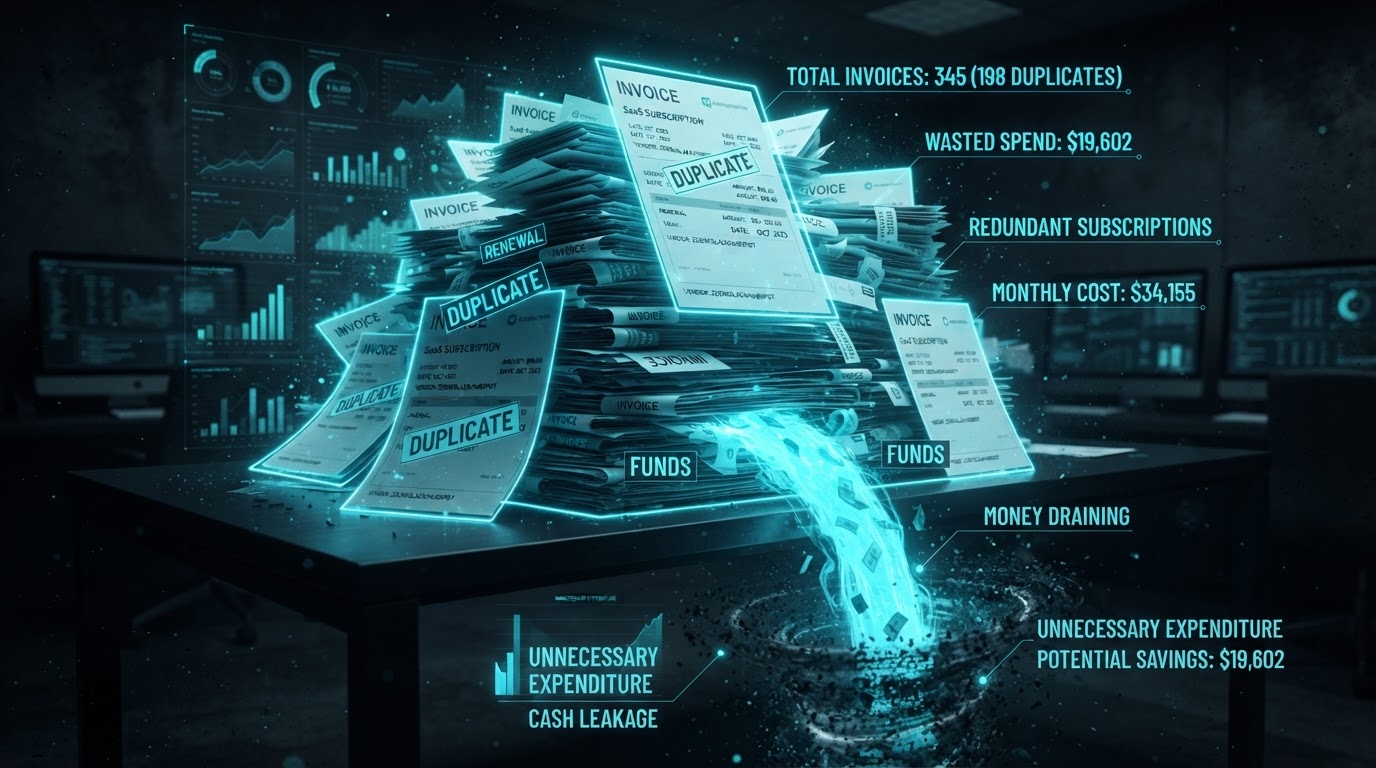 ROI
60%+ wasted spend on duplicate, unsanctioned SaaS AI subscriptions. Shadow tools compound monthly with zero governance oversight.
Not ready for the full 30-day audit? Get a no-cost, read-only scan teaser of your external AI attack surface. We map publicly exposed LLM endpoints, leaked non-human credentials, and unsanctioned SaaS AI subscriptions — delivered as a one-page brief within 24 hours.
Four board-ready work products, delivered in 30 days. Each maps directly to an executive decision and a quantified risk reduction.
Live discovery of every sanctioned and shadow AI endpoint across SaaS, cloud, and on-prem estates. Interactive graph highlights unmonitored agents and credential sprawl in real time.
OWASP Top 10 mapped. Sandboxed red-team of your agentic stack exposing injection, privilege, and exfiltration paths.
Prioritized gaps mapped to controls, evidence requirements, and a remediation roadmap your board can sign off on.
Consolidate duplicate AI spend into a governed stack with a quantified ROI realization model.
How the 30-Day Executive AI Audit shifts mid-market enterprises across manufacturing, SaaS, life sciences, energy, telecom, and more — from unmonitored sprawl to a governed, board-ready AI estate.
 Financial Services
Before: Advisors spent 35% of their day manually synthesizing research across 7 disconnected platforms; client onboarding took 14 business days.
After: Governed research-synthesis agents cut onboarding to 48 hours with zero SEC compliance findings.
 Logistics & Operations
Before: Manual vendor exception handling and SAP/WMS inventory re-routing caused 6.5% stockout rates across distribution centers.
After: Automated exception triage reduced stockouts to 1.8% and cut disruption response time by 82%.
 Healthcare & Regulatory
Before: Clinical document drafting relied on unmonitored AI tools with no immutable audit logs, risking FDA and HIPAA exposure.
After: ISO 42001-aligned clinical drafting with cryptographic audit trails sped regulatory audits by 65%.
 Commercial & Revenue Ops
Before: CRM pipelines were manually enriched from email and call telemetry; month-end close took 5 days with duplicate AI tool spend.
After: Auto-enriched pipelines and governed CPQ approvals compressed close to 4 hours and consolidated 3 redundant SaaS licenses.
 Procurement & Legal
Before: Contract risk scoring and vendor questionnaires were handled manually with unscoped AI agent tokens accessing ERP data.
After: Automated risk scoring and redline workflows cut contract review time by 80% with scoped, rotated non-human identities.
 Energy & Utilities
Before: Unmonitored AI agents optimizing grid load had write access to SCADA thresholds with no human-in-the-loop gate.
After: Zero-trust approval gates on all SCADA-bound agent actions eliminated logic manipulation risk with zero downtime.
 Technology & Startups
Before: Engineering, sales, and ops independently purchased 6 overlapping AI coding and writing tools with no procurement oversight.
After: Stack rationalization consolidated to 2 governed tools, preserving $340k in annual operating capital.
 E-Commerce & Retail
Before: Demand-forecasting agents ran on unscoped API keys with no drift detection, causing stock imbalances across SKUs.
After: Governed forecasting with drift circuit breakers tripled inventory turn and eliminated phantom stockouts.
 Telecommunications
Before: Billing reconciliation across legacy BSS systems used autonomous agents holding persistent, unrotated API credentials.
After: Scoped, offboardable agent identities with immutable ledger writeback achieved 99.4% reconciliation accuracy.
 Construction & Real Estate
Before: BIM digital-twin agents processed vendor models with no prompt-injection scanning, risking corrupted project logic.
After: Sandbox red-teaming and OWASP ASI01 patching secured BIM workflows, cutting design cycles by 60%.
High-impact analysis from our AI advisory practice for security and revenue leadership.
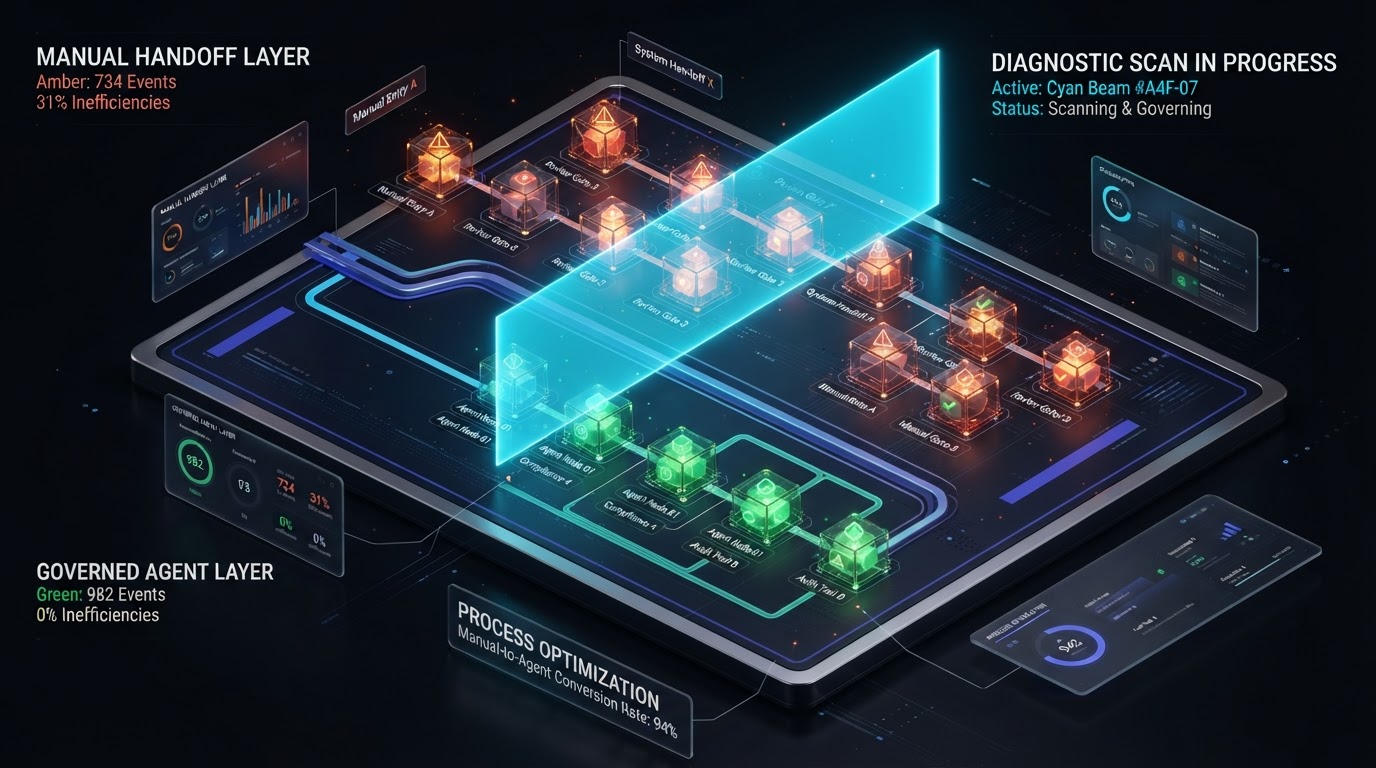
What an AI Audit Actually Does Under the Hood
Read article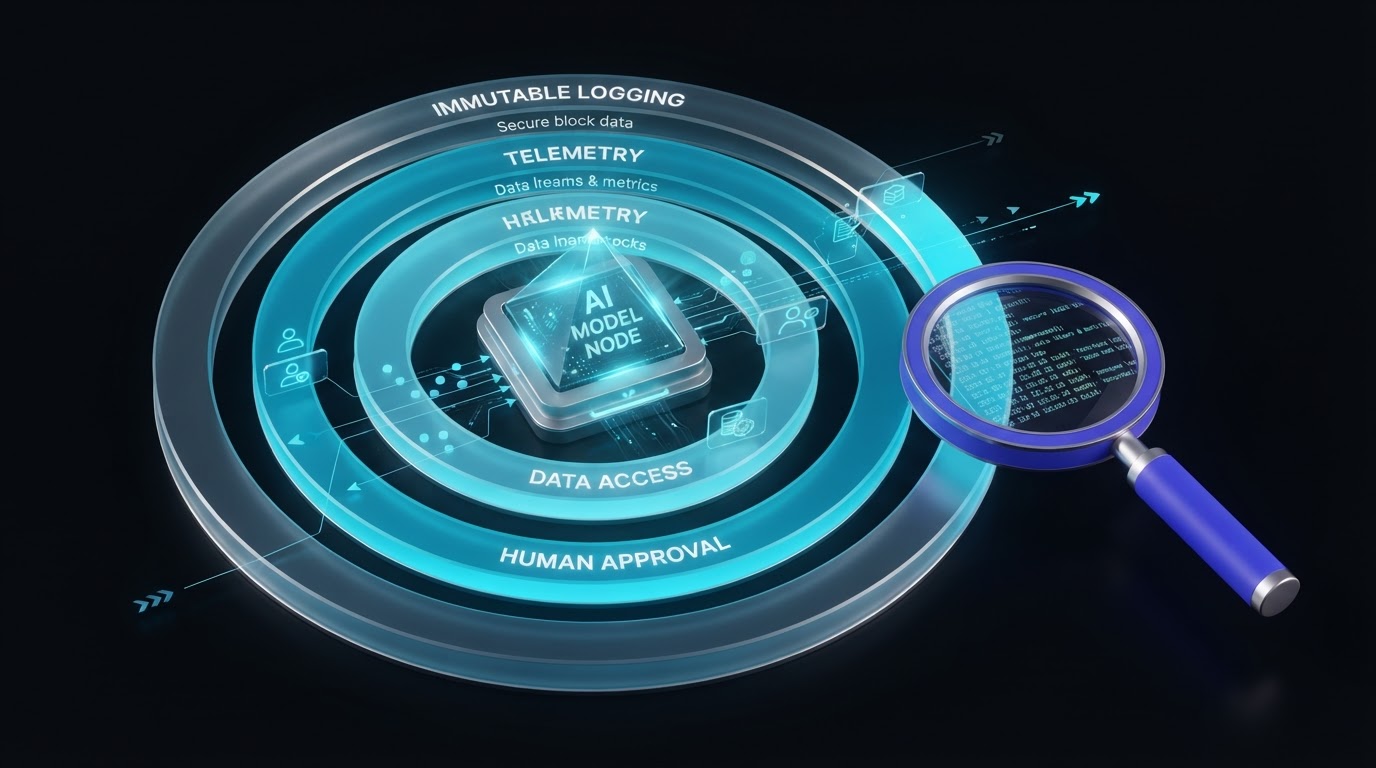
How an AI Audit Preserves Enterprise Valuation
Read articleHow Governed AI Accelerates Enterprise Growth
Read articleA 30-day institutional diagnostic for CISOs, CIOs, and executive boards — delivered as six board-ready work products scoped to your endpoint & system architecture.
NorthForge Group · AI Advisory
Passive network discovery flagging every unsanctioned AI SaaS, browser plugin, & multi-agent token.
Red-team sandbox simulation testing indirect prompt injection (OWASP ASI01), privilege escalation & token sprawl.
Audit-committee ready compliance matrix mapping Article 14 human oversight & cryptographic logging gaps.
Eliminates duplicate SaaS AI tool spend, providing a quantified ROI realization model for CFO signoff.
Polished board briefing with executive summary, vulnerability topology, and remediation budget.
2-hour interactive working session with Sagar Kulkarni & NorthForge principals to execute remediation.
🔒 Standard NDA required prior to discovery scan · Zero downtime · 100% passive monitoring
Yes. Every engagement begins with a mutual NDA. All findings, telemetry, and deliverables are handled under strict confidentiality and scoped data-handling agreements. We never retain client telemetry beyond the engagement window.
The discovery and endpoint scan is zero-downtime and passive by design. We read metadata, configuration, and network telemetry without modifying production systems. Active penetration testing occurs only inside an isolated sandbox against copies of your agentic stack — never against live systems.
Minimal. We require read-only API access to your SaaS and cloud estates, and a securely scoped agent for on-prem endpoint discovery. Most clients complete onboarding in under two days with a single technical point of contact on your side.
Yes. The package includes a board-ready presentation deck and a live walkthrough session with your CISO and executive team. We attend your board or audit committee meeting to present findings and the remediation roadmap.
Scope scales with enterprise size and endpoint count — from smaller mid-market estates to larger multi-site or regulated environments. A fixed engagement plan is provided after a 30-minute scoping call.
Most engagements kick off within one week of a signed engagement letter. Passive discovery runs immediately on scoping call completion; the full 30-day deliverable matrix lands within four weeks.